


Deepfakes have shifted from novelty to real risk for employers. Read on to learn more about how to protect your company and avoid falling for a fake.
Who Did We Hire?
Some identity fraud research indicates that overall deepfake and synthetic identity fraud attempts targeting organizations have surged globally. According to a report by GetReal Security, 41% of IT, cybersecurity, risk, and fraud leaders say their company has hired and onboarded a fraudulent candidate.
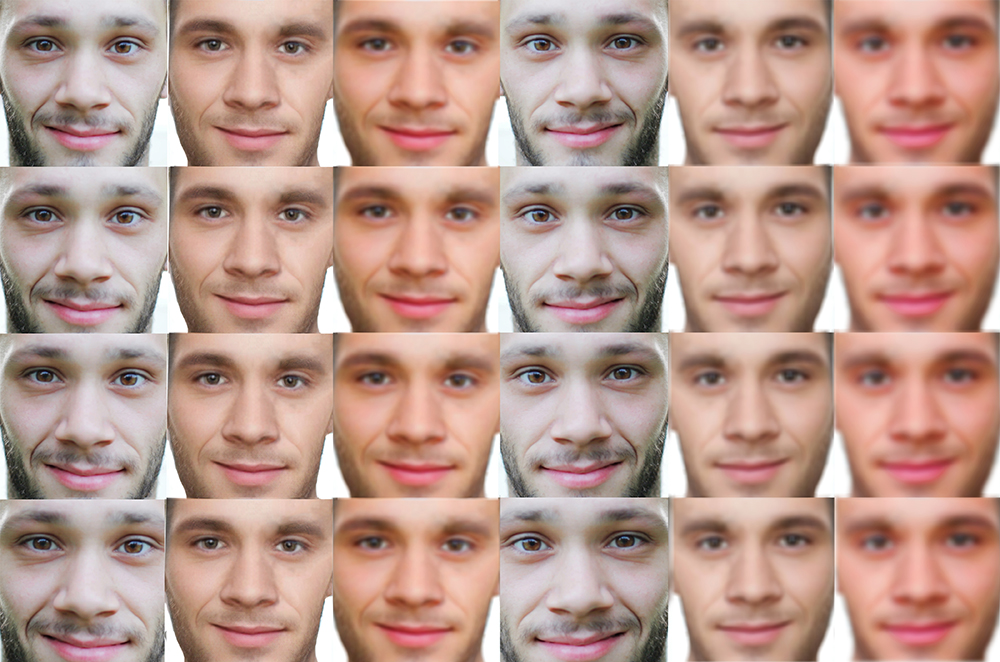
Recent reports detail this growing trend of remote interviewees using synthetic video and voice to pass identity checks, while security researchers and training providers have documented cases of imposters attempting to infiltrate U.S. companies as “IT workers.” The Federal Bureau of Investigation (FBI) has warned of a rise in deepfake-enabled fraud in remote hiring, and high-profile incidents show how convincingly artificial intelligence (AI) can simulate live presence, senior executives, and credentialed professionals.
In addition to a public service announcement on December 19, 2025, warning about the rise in AI deepfake impersonation, the U.S. State Department and the FBI, together with multiple countries’ foreign affairs and other government offices, issued a joint alert on July 31, 2026, to countries, U.S. businesses, and other entities, notifying them that the North Korean government has deployed IT services workers to obtain false identities and remotely earn income to fund North Korea’s unlawful nuclear weapons and ballistic missile programs.
The joint alert says that “these workers seek out contracts with the intent of remitting their salaries to their parent North Korean agencies. They also pose an insider threat to companies and are involved in data exfiltration, cryptocurrency theft and theft of sensitive information.” North Korea is a sanctioned jurisdiction, of course, meaning that U.S. companies are prohibited from employing workers from North Korea. The FBI has also reported that eight individuals have been sentenced to prison in 2026 alone for their roles in these schemes.
Case In Point
Cybersecurity awareness training company KnowBe4, which trains companies on how to avoid getting hacked, hired a deepfake job applicant as a software engineer. The fake job applicant used the stolen identity of a U.S. citizen when applying for the job—enhanced by AI—and had four video interviews while using AI-deepfake technology.
The fake job applicant was a North Korean government operative. Once hired, he requested to have his laptop shipped to an address that was, in fact, an “IT mule laptop farm.” He then used a virtual private network (VPN) from North Korea or China and attempted to hack into KnowBe4’s computer systems to plant malware before his actions were discovered and thwarted by KnowBe4.
There was also the notorious case of the finance employee in Hong Kong who was duped on a work video call by a deepfake “chief financial officer” (CFO) and deepfake “colleagues” and wired roughly $25 million to criminals who had created the deepfake video and voice replication of the employee’s CFO and colleagues.
What Should Employers Do Now?
Here are just a few practical suggestions to help mitigate the risk that deepfakes will affect your workplaces and when to call legal counsel:
- Treat deepfake hiring as both a security and a legal exposure.
- Conduct candidate interviews in-person whenever possible.
- Standardize identity assurance at every hiring stage with layered controls.
- Verify references independently by telephone, not just email, and cross-check LinkedIn or other professional networks to verify employment history and professional connections.
- Background checks should cross-verify information from multiple sources. For instance, check that verified addresses for the candidate match those where laptops are being sent.
- For sensitive roles, such as those who will have access to your electronic systems’ back end, add post-hire safeguards.
- Require new hires to meet their supervisors and/or HR in-person, and where permitted by law, use geolocation verification and required check-ins for remote workers to confirm they’re working from where they say they are.
- Train your internal recruiters to spot “red flags” in job candidates interviewing by video to identify and respond to such tactics, including audio and video that don’t sync at the same time; seemingly scripted answers; and refusal to perform real-time gestures, such as looking up and looking down while on camera, then escalate your concerns to security, legal, and compliance.
- Call employment counsel immediately if a candidate fails identity checks, if you plan to withdraw a conditional offer, or if you see indicators of a sanctions nexus or decide to take any adverse action that relies on biometric or identity-proofing results.
The takeaway for employers is clear: The combination of remote-first recruiting, outsourced screening, and generative AI tools has created a new class of insider threat: someone you never actually intended to hire.
If you have any questions or seek legal advice on mitigating legal and operational risk with these kinds of issues, please contact Lisa Brauner in Whiteford’s labor and employment law department at lbrauner@whitefordlaw.comor 646-618-8655, or contact any member of Whiteford’s labor and employment law team.